Learn to Spoof IP Address With RafaleX and Engage Packet Builder

The RafaleX application allows for the creation of custom IP packets. The packet is very customizable and allows for the spoofing of the IP, setting the flags, number of packets, and so forth. RafaleX is becoming hard to locate on the Internet as it appears it is now called Engage Packet Builder.
The RafaleX application is an excellent way to “spoof” custom packets. Attackers can place a valid IP address as the source of the packet and the target will have to attempt to respond to the spoofed address. By sending hundreds of thousands of packets in this manner, an attacker can create a Denial of Service attack against a target.
In this example, the Source IP of the packets to be sent is set to 10.10.10.10 with the source address of port 123. According to Internet etiquette, this should never be able to route on the Internet as the 10.x.x.x range is reserved for Private addressing. Set the destination IP to the target address. In this example it is 172.16.1.40. Set the Destination
port to port 21. The SYN and ACK flags were set for each packet.
*Note: The Ethernet communications process requires a three-way handshake:
SYN: Synchronize
SYN-ACK: Synchronize-Acknowledge
ACK: Acknowledge
When a computer receives an uninitiated SYN-ACK packet its response is to send a RST (Reset) packet.
The RafaleX application is an excellent way to “spoof” custom packets. Attackers can place a valid IP address as the source of the packet and the target will have to attempt to respond to the spoofed address. By sending hundreds of thousands of packets in this manner, an attacker can create a Denial of Service attack against a target.
In this example, the Source IP of the packets to be sent is set to 10.10.10.10 with the source address of port 123. According to Internet etiquette, this should never be able to route on the Internet as the 10.x.x.x range is reserved for Private addressing. Set the destination IP to the target address. In this example it is 172.16.1.40. Set the Destination
port to port 21. The SYN and ACK flags were set for each packet.
*Note: The Ethernet communications process requires a three-way handshake:
SYN: Synchronize
SYN-ACK: Synchronize-Acknowledge
ACK: Acknowledge
When a computer receives an uninitiated SYN-ACK packet its response is to send a RST (Reset) packet.

The number of packets was set to 100. Click the Send button to send the packets to the target. The Status area at the bottom left of the application will tell you that the packets were sent.

The proof is below screen shot captured from packet capturing tool:


NOTE TO THE READERS :
This Tutorial is for educational purposes only and any actions taken By you after reading this post is all upon you. IHA takes no Charge of the Effects hereafter.
THANK YOU FOR READING
Crack BIOS password

There are a lot ways to Crack the BIOS password. This is one of them but I would say that this one ismore effective than the rest because the rest of the ways does not Guarantee you that it will Crack the BIOS password while in this case the Cracking is Guaranteed since in this we will remove the functionality of password protection of the BIOS.
Follow the steps below :
1) Boot up windows.
2) Go to command prompt directly from the windows start up menu.
3) Type the command at the prompt :
debug
4) Type the following lines now exactly as given . . . .
o 70 10
o 71 20
quit
exit
4) Exit from the dos prompt and restart the machine.
Password Protection Gone ! ! !
PS: I tested this in Award Bios . . .
There seems to be some issue regarding display drivers on some machines if this is used. Just reinstall the drivers, Everything will be fine………..I have not found any other trouble if the codes are used. o be on safe side, just back up your data. The use of this code is entirely at ur risk. It worked fine for me.
How to trace pc from ip address and know location from chatting online
this can also be said as tracing a person by knowing his/her Ip address so lets begin the tutorial.
1st step:
First of all you need to make the person online or you you need to chat with him via any social networking site
like Facebook,G-mail,Orkut or via any messenger like yahoo messenger, Facebook messenger, Skype...etc.you type your message like hi or hello and wait till you get reply from another side.

2nd step :
after getting response from your friend
now you need open command prompt or cmd and then type this command netstat -a
if you are using any messenger then better go for this dos command netstat -nbt

Now carefully watch the ip address and get the victim's ip address...

After knowing the ip address you can easily trace the location of the victim's computer.
Go to this site.http://www.whatismyipaddress.com/ Or
http://www.ip-address.org/ to locate the correct location
You can compare the User details and the IP details and traceout user's IP adress.
How To Be Safe Facebook Account From Hackers
Hello
Friends,
Do You know
about 6,00,000 facebook accounts got hacked daily.Its very easy to hack a
facebook account coz hackers are introducing new methods day by day to crack
your system's security thats why i am Writing a article oncountermeasures to
avoid hacking.so lets start.
·First of
all log in to your facebook account then go to account settings then after go
to security tab.
·In security
tab.the first options says.Secure Browsing: Enable it.when You use secure
browsing.Your Default Connection Sets To Https Insted of Http.
Http Stands
For Hyper Text Transfer Protocal. When We use Http Our Browser And Server
Create Communication In Normal Language. But On the Other Hand Https stands For
Hyper Text Transer Protocal Secure, When We Use Https Browser and Server Talks
In encrypted Language. So Possibility Of Man In Middle Attack Gets Reduced. In
'MIMA' a Third Person or Brodly Says Hacker Can Listen The Communication
Between Browser And Server.
·Now Come To
second Point,Again Go To account settings then after go to security tab.
·In security
tab.the Second options says.
LOGIN NOTIFICATIONS: Enable Login
Notifications.
Note: Enable Both Email And Phone
Notifications.
It is Necessary To enable Login
Notifications Because facebook can notify you when your account is accessed from a computer or mobile device
that you haven't used before.
Now Settings
Part is Completed.
So Lets
Begin To Avoid The Possible Technique By Which Hacker Can Hack Your Account.
·First of
All Keep Your Primary Email Address Password diferent from facebook password
never Keeps Both Password Same. Think if
Someone Hacks Your facebook account and change Your facebook Password Also Then You can Get Back Your
Password By Clicking On forget Password link.But If Both Password Are Same.Then Anybody can Change
Both Passwords easily and You will Lose Your Accounts For Forever. :(
·Many
Childrens Also Known as n00bs Hackers Hack Accounts Via Phishing.Phishing is an
e-mail fraud method in which the hacker
sends out Exactly Same Looking Website Address in an attempt to gather personal and financial information from
recipients.
So Never Give Your Creditials On false
Websites. If Anyone give You link Like... Faecbook.com Or Facbook.com Then Never Give Your Email
address and Passwords there.
Always Do Your Password To Only Facebook.Com
Otherwise You Will Be hacked.
·Keylogging
Is Also A method By Which Anyone Can Got Easily Haked.The Entire Process Is
known As Keylogging and The Software
Used In it known as keylogger.Keylogger is most intelligent tool to secretly capture all typed keystrokes
activities of your kids, employees, family members, relatives, friends on computer system.
To Avoid keylogging. Always Use a Good License
Version Antivirus Software and Regularly Update
and Scan With It.
·Always Give
A unpredictible Security Question Answer.
·Never
Add Unknown Persons In Your
Account.Facebook Have A Vulnerablity To bypass Security By Using Of Your Three Friends.
·Lastly I
will Talk About Countermeasures for Trojan. Trojan Are Dangerous Kinds Of virus
They Can Work As Keyloggers And Hacker
Can Also acess To Your System.To Avoid Hacking With Trojan. Always Use a Good License Version Antivirus Software
and Regularly Update and Scan With It.One More
Important Thing Trojan Can Be Binded Or crypted With Any
Software,Image,Video Or Any Kind of File
That Makes Them Undetectable.So Never Download Anythings From suspected
Sites Like ziddu Or Mediafire.
So Guys...The Post Is Over...Be Safe..Be Happy
:) !!!
How to delete multiple Facebook messages at a time

Instead of deleting one messages at a time, you can delete all selected messages at a time.
If you are using Chrome browser just follow steps ......
There is a handy extension for Google Chrome.

Step 1: Download a copy of the Facebook Fast Delete Messages extension.
Step 2: Log in to your Facebook account and head to the Messages area
Step 3: Click the small Red X next to each message to delete the entire thread without having to open it.
After installing the extension your facebook messages will look like this

This extension still makes message deletion faster than Facebook's method.
10 Operating Systems You Might Not Know About
10.Darwin
Darwin is an open source POSIX-compliant computer operating system released by Apple Inc. in 2000. It builds on BSD and includes the kernel, and core system utilities. Darwin in itself is a complete operating system. Apple build on Darwin to create OSX, iOS, and AppleTV,which is something that not many people are aware of. It was used to create the 32-bit ARM processor used in the iPhone, iPod Touch and iPad as well.

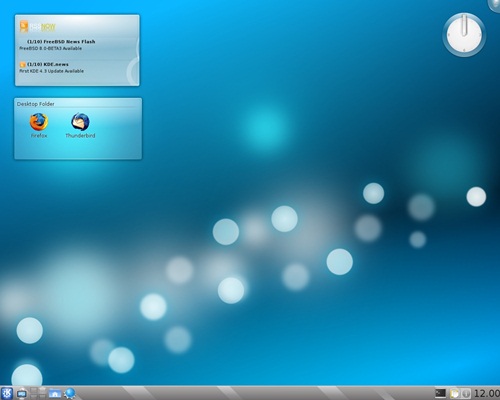
9. FreeBSD
FreeBSD is an advanced operating system for modern server, desktop, and embedded computer platforms. Its development started in 1993 and in FreeBSD 2.0 was released in late 1994.FreeBSD’s code base has undergone over thirty years of continuous development, improvement, and optimization. It is also used by some of the world’s busiest web sites and most pervasive embedded networking and storage devices.Out of all BSDs,FreeBSD is the most used. It’s most recent release was in January 12, 2012.
8. ReactOS
ReactOS is a free, modern operating system based on the design of Windows XP/2003. It is not a Linux based system, and shares none of the unix architecture. ReactOS has been designed for high security; it doesn’t share some of the common security flaws with other operating systems. ReactOS has been noted for its information on undocumented Windows APIs and more generally as an open-source drop-in replacement for Windows. It was first released on July 20, 1998 and its most recent release was on February 7, 2012.

7. Solaris
Solaris was orignally developed by Sun Microsystems but after Oracle Corportaion’s acquistion of Sun Microsystems in January 2010 it has been as Oracle Solaris. Solaris is known for its scalability, especially on SPARC systems, and for originating many innovative features such as DTrace, ZFS and Time Slider. It was first released in June 1992 and its most recent release was on November 9,2011.

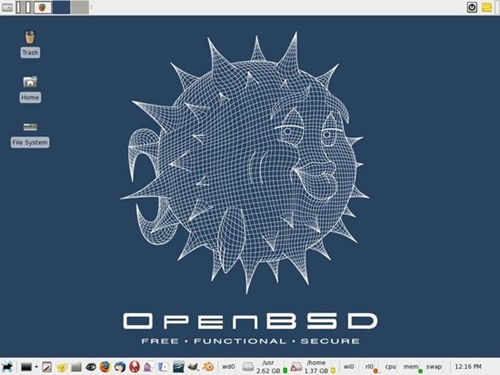
6. OpenBSD
OpenBSDis a free open source operating system based upon the Berkeley Software Distribution (BSD) for UNIX. OpenBSD evolved from NetBSD and also runs on a variety of hardware. It also pays alot of attention towards the security of the content provided by the users and constantly works around to fix any of the problems that may affect the users. Users may also report their problems with it to them. It was first released on 1 October,1996 and it’s most recent release was on 1 November,2011.
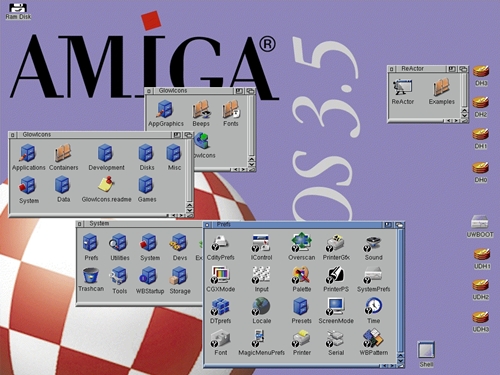
5. AmigaOS
AmigaOS is the default native operating system of the Amiga personal computer. Amiga Inc. was founded in 1982. The Amiga was developed first as game console. It was developed first by Commodore International, and initially introduced in 1985 with the Amiga 1000. Currently,its intellectual properties belong to Amiga Inc. Its most recent release was on 22 December,2011.
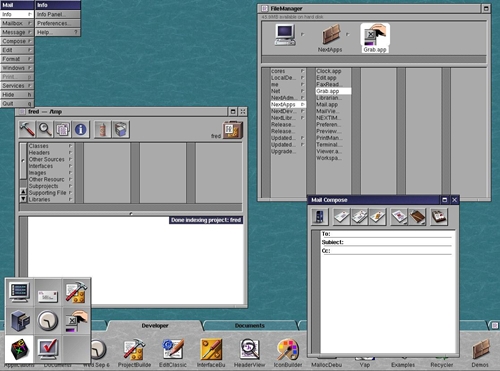
4. NEXTSTEP
NeXTSTEP was the object-oriented, multitasking operating system developed by NeXT Computer to run on its range of proprietary workstation computers, such as the NeXTcube. This was at the time when Steve Jobs left Apple in 1986, he then started NeXT. He wanted a computer that would run on Research Labs ,Universities,Colleges,etc. He envisioned it to be the Market leader in Science. It was based on the Mach kernel and 4.3BSD Unix. It was first released in September 18, 1989 and the last update it recieved was in 1995.
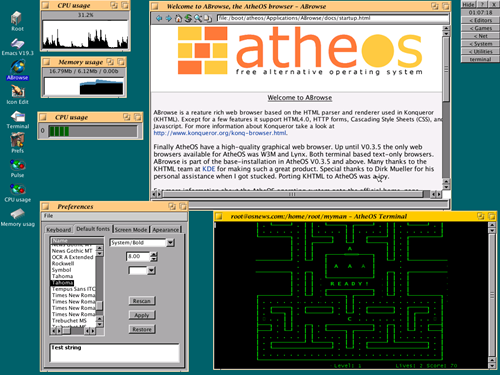
3. AtheOS
AtheOS was a free and open source operating system for x86-based computers. AtheOS currently runs on Intel, AMD and other compatible processors and support the Intel Multi Processor architecture. AtheOS was created by a Norwegian programmer, Kurt Skauen and it was announced to the world in March 2000.
2. SkyOS
SkyOS was a prototype commercial, proprietary, graphical desktop operating system written for the x86 computer architecture. It was made by Robert Szeleney over a span of 10 years. The SkyOS, on the surface, resembles Microsoft Windows but has features–such as protected memory, symmetric multiprocessing, multitasking, and multithreading, which Windows lacks. It’s last release was on August 3, 2008.

1. Slax
Slax is a LiveCD Linux distribution based on Slackware and is currently being developed by Tomáš Matějíček.its ease of customization is one of its biggest benefits.Slax modules are compressed read-only SquashFS file system images that are compressed with a LZMA compressor. Slax’s slogan says, “your pocket operating system”. The most recent release of Slax was on 4 August 2009.
Subscribe to:
Posts (Atom)